TiVerify
Tier Verify: a supplier credentialing thesis for digital government, so status can be issued, checked, and trusted without a manual queue.
What this is
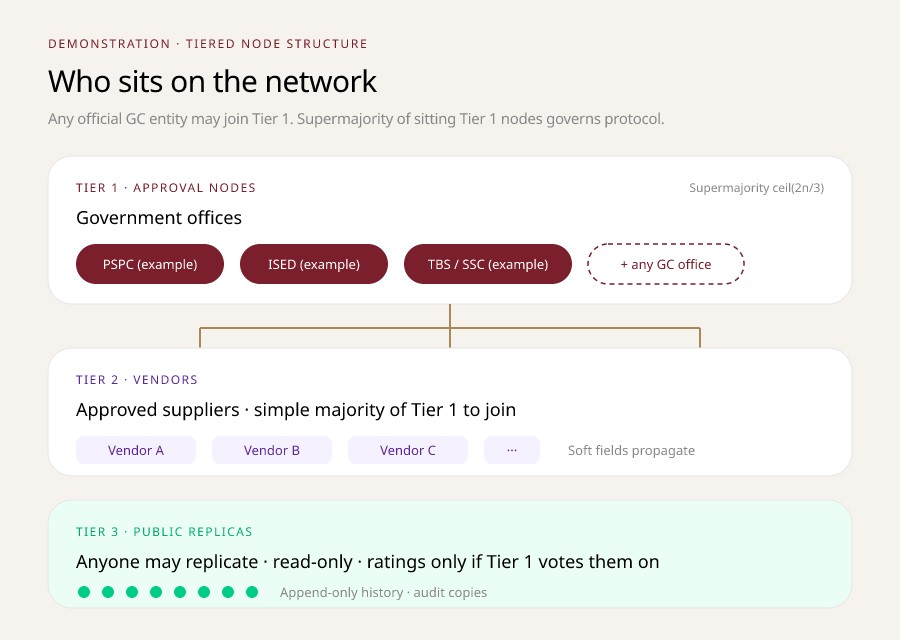
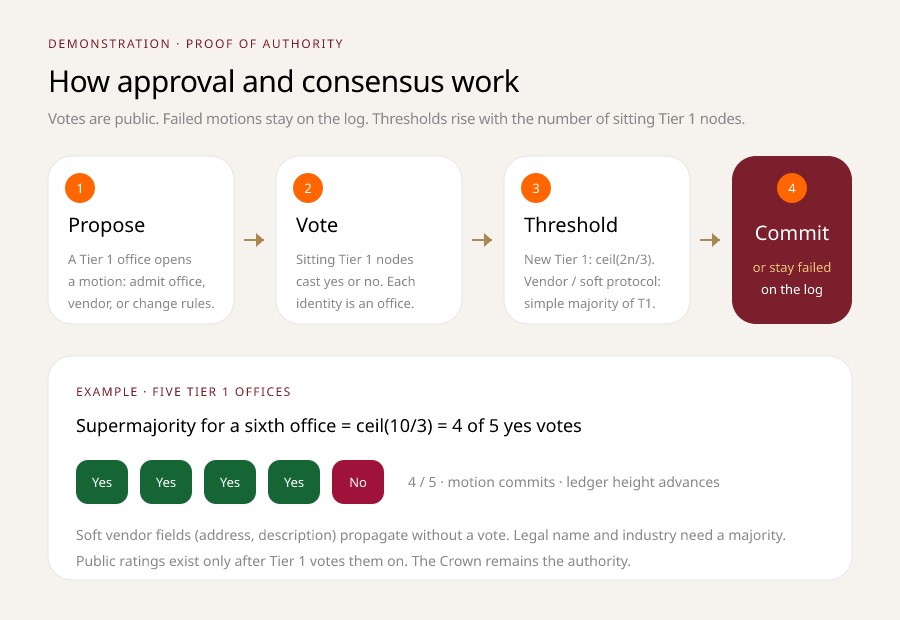
TiVerify (Tier Verify) is a trust and verification concept for digital government. It treats supplier status as a credential that can be issued, presented, and checked: tamper-resistant records, embeddable trust indicators, and a path for agentic systems to verify counterparties without waiting on a human queue. A demonstration is available on request. Reach out through Engage if you want to see it.
Why it matters
Governments buy from thousands of suppliers. Verification that still depends on screenshots, inboxes, and manual lookup cannot keep pace with digital procurement, let alone with software acting on an organisation’s behalf. Cryptographic credentials and a clear directory of status make trust inspectable. That is civic infrastructure: boring when it works, expensive when it fails.
The problem it addresses
Supplier verification and decentralized credentialing remain slow, centralized, and hard to embed. Buyers cannot see status at the moment of a decision. Suppliers cannot self-serve proof. TiVerify asks what a Canadian-operated credentialing layer would look like if issuance, one-click or scan verification, and revocation were first-class outcomes rather than PDF attachments.